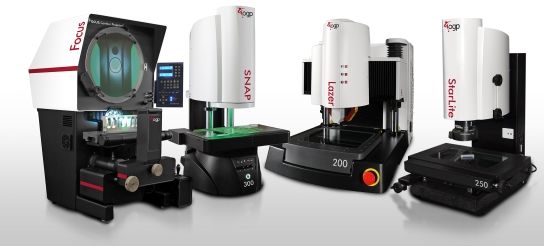
Product Selector
Click-to-answer questions guide you through selecting the right product for your application.
Coordinated Vulnerability Disclosure Policy
Quality Vision International (QVI) is committed to maintaining the security of our products and software. We welcome reports from customers, security researchers, partners, suppliers, and others who identify potential security vulnerabilities.
This policy supports QVI’s vulnerability handling obligations under the European Union Cyber Resilience Act (Regulation (EU) 2024/2847)
Scope
This policy applies to security vulnerabilities in QVI products with digital elements, including software, firmware, embedded software, and related product components.
For product issues that do not have a security impact, please use our normal technical support channels: Service & Support
Reporting a Vulnerability
To report a potential security vulnerability, contact the QVI Product Security Incident Response Team (PSIRT): [email protected]
Or select the Report a Vulnerability option on the Technical Support Request Form: Technical Support
Please provide as much of the following information as is reasonably available:
What You Can Expect From QVI
QVI will review reported vulnerabilities and, as appropriate:
The time required to investigate and resolve a vulnerability will depend on its complexity, severity, affected products, and available mitigations.
Coordinated Disclosure
We ask reporters to give QVI a reasonable opportunity to investigate and address a reported vulnerability before publicly disclosing technical information that could increase risk to customers.
QVI will coordinate vulnerability handling and disclosure in accordance with applicable requirements and timelines of the European Union Cyber Resilience Act, including applicable regulatory reporting obligations.
When appropriate, QVI may publish a security advisory or otherwise communicate information necessary for customers to understand and address a vulnerability.
Last reviewed: August 2026
Next review: June 1, 2027